Project
ICV OSS: AN OPEN-SOURCE DJANGO PACKAGE ECOSYSTEM
Seven open-source Django packages on PyPI plus a private catalogue, each its own repository with …
The commercial home for django-waf: a self-hosted web application firewall and a collective threat feed, built on the idea that security should be inspectable, not fear-driven.
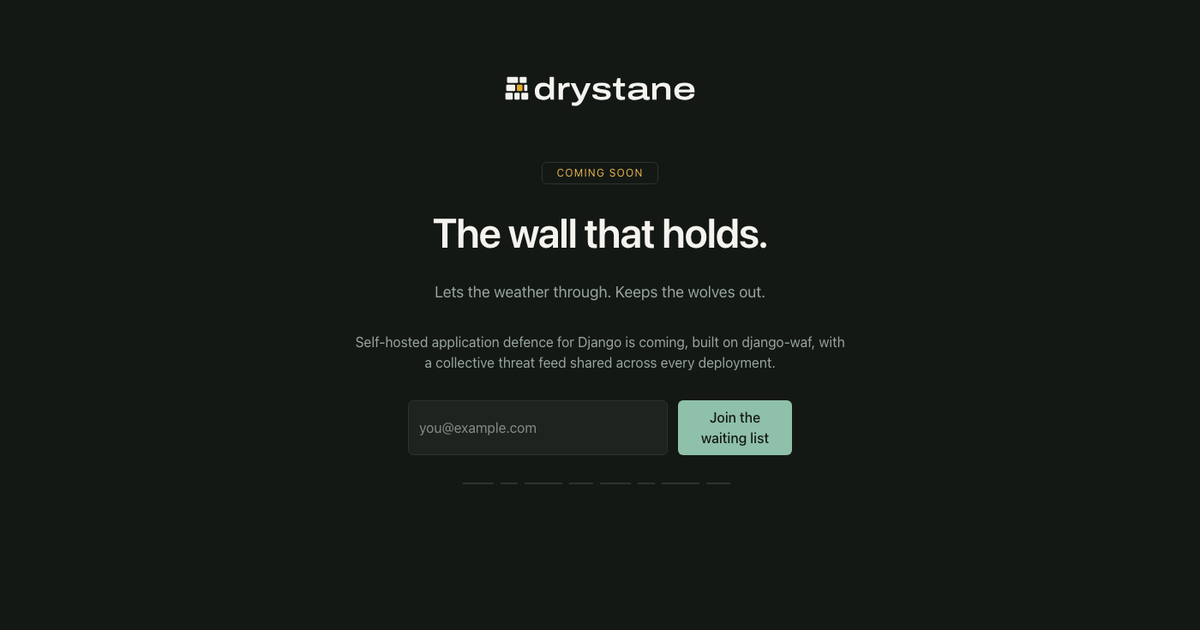
Drystane is the commercial site and feed service for django-waf, and the reference deployment I dogfood the firewall against. It is a marketing site, a waiting-list capture flow, and a collective threat-feed API served from threats.drystane.com.
The brand idea is a drystane dyke, a dry-stone wall built without mortar: calm, inspectable, self-hosted security in a market that mostly sells fear. Every rule is visible; nothing is proxied through an opaque third party.
Commercial web application firewalls tend to be opaque, SaaS-proxied, and marketed on fear. django-waf takes the opposite position: self-hosted, transparent, and Django-first but not Django-only. Drystane gives that position a home, and adds a collective threat feed so that every deployment can learn from what struck the others.
Drystane is a small, focused Django project: Tailwind, Alpine.js, and HTMX on the front, PostgreSQL and Redis behind it. The django-waf middleware sits directly after Django's own security middleware, and the waiting-list form uses the firewall's form-protection subsystem (render token, honeypot, and time trap), so the product is genuinely dogfooded rather than merely demonstrated.
The threat feed is built to a published wire contract. API keys are stored only as a hash of an opaque token, never in the clear. The feed and the marketing site are split across two hosts by a small host-aware routing layer, and the feed models are deliberately free of auth assumptions so an accounts system can claim installs later without a redesign.
Drystane is pre-launch. The live surface is the marketing site and waiting-list capture; the threat-feed API is built to its contract as a working MVP and has not yet been opened to the public. Seed threat sources and licence-compliant attribution are in place, with confidence scoring that will be refined against real telemetry once the feed is live.
Seven open-source Django packages on PyPI plus a private catalogue, each its own repository with …
A padel-first platform bringing players, coaches, clubs, and suppliers onto one system, with free tools …
A multi-tenant CMS and commerce platform using PostgreSQL schema-based isolation, with a headless content API …
£900/day · Available for projects · Usually responds within 24 hours